 Bryan Needs a Title for His Home Page



Hot tip on AI agents and email.
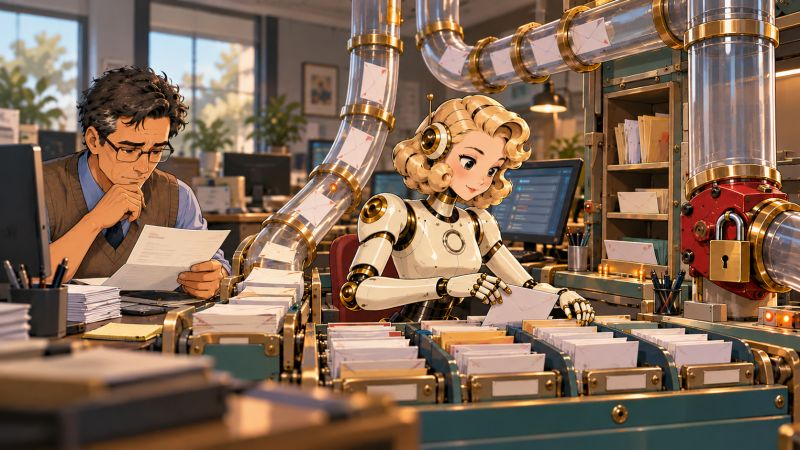 Everyone’s racing to give their AI agent access to their inbox. I get it, the productivity pitch is compelling. But you’re handing an unpredictable system the keys to your professional reputation, and one hallucinated reply-all is all it takes and contrary to any promised miracle prompt, you should not be using the agents own failure risk as your only safeguard.
There’s a cleaner way to do this, and it’s not new architecture. It’s how competent mail admins have handled delegation for decades.
Set up your AI agent with its own email account. Not yours. Its own. Then lock that account down. Restrict the account it uses to internal recipients only, or whatever boundary makes sense for your environment. Let the built in platform permissions do the job they were built for.
Then give the agent delegate access to the mailbox you actually want it working on. Don’t give it permission to “Send As…”.
Now your agent can read inbound mail. It can sort, triage, summarize, and flag. It can fire off internal alerts, email another team mailbox, update a dashboard, trigger a workflow. The sky’s the limit on what you build downstream.
What it can’t do is send an email from your account to a client at 2 AM that you have to explain on a call at 8.
One implementation note for the admins in the room: this is straightforward in Exchange, where Reviewer permissions give you folder-level read-only access. Google Workspace is a different story… Gmail’s built-in delegation grants read, send, and delete as a package. To get true read-only in Google’s ecosystem, you’re looking at the Gmail API with a gmail.readonly scope, which is a different implementation path but absolutely achievable. Other platforms will have other solutions but I hope this gives you the general idea.
The principle is the same regardless of platform: separate the reading from the sending. Give the agent eyes on the work and give them only the rope they need to do the job.
A word of caution: even read-only isn’t risk-free. Depending on the mailbox, your agent could still process privileged content: legal correspondence, HR matters, financials, medical, etc… Compliance teams in regulated environments will want even read access scoped too, not just handed over wholesale.
And the agent’s own mailbox? That’s a surface worth thinking about. If it can send internally, people on your team are now receiving mail from an AI… and they may not realize it. Labeling and monitoring that outbound account matters more than you’d think. You’ll also want to force a mandatory footer notice or even better make the mailbox name something obvious as to its purpose.
Those secondary concerns deserve their own post. For now, start here: the tooling already exists, the permissions models are built in, and you don’t need a new product. You need someone who understands infrastructure to set it up right.
There’s a cleaner way to do this, and it’s not new architecture. It’s how competent mail admins have handled delegation for decades.
Set up your AI agent with its own email account. Not yours. Its own. Then lock that account down. Restrict the account it uses to internal recipients only, or whatever boundary makes sense for your environment. Let the built in platform permissions do the job they were built for.
Then give the agent delegate access to the mailbox you actually want it working on. Don’t give it permission to “Send As…”.
Now your agent can read inbound mail. It can sort, triage, summarize, and flag. It can fire off internal alerts, email another team mailbox, update a dashboard, trigger a workflow. The sky’s the limit on what you build downstream.
What it can’t do is send an email from your account to a client at 2 AM that you have to explain on a call at 8.
One implementation note for the admins in the room: this is straightforward in Exchange, where Reviewer permissions give you folder-level read-only access. Google Workspace is a different story… Gmail’s built-in delegation grants read, send, and delete as a package. To get true read-only in Google’s ecosystem, you’re looking at the Gmail API with a gmail.readonly scope, which is a different implementation path but absolutely achievable. Other platforms will have other solutions but I hope this gives you the general idea.
The principle is the same regardless of platform: separate the reading from the sending. Give the agent eyes on the work and give them only the rope they need to do the job.
A word of caution: even read-only isn’t risk-free. Depending on the mailbox, your agent could still process privileged content: legal correspondence, HR matters, financials, medical, etc… Compliance teams in regulated environments will want even read access scoped too, not just handed over wholesale.
And the agent’s own mailbox? That’s a surface worth thinking about. If it can send internally, people on your team are now receiving mail from an AI… and they may not realize it. Labeling and monitoring that outbound account matters more than you’d think. You’ll also want to force a mandatory footer notice or even better make the mailbox name something obvious as to its purpose.
Those secondary concerns deserve their own post. For now, start here: the tooling already exists, the permissions models are built in, and you don’t need a new product. You need someone who understands infrastructure to set it up right.